> ## Documentation Index
> Fetch the complete documentation index at: https://docs.mka1.com/llms.txt
> Use this file to discover all available pages before exploring further.
# API keys
> Create an API key and authenticate server-side MKA1 requests.
Already have a key? Go directly to the [quickstart](/docs/quickstart). Your administrator supplies the API gateway address for a private deployment.
## Create a key in the console
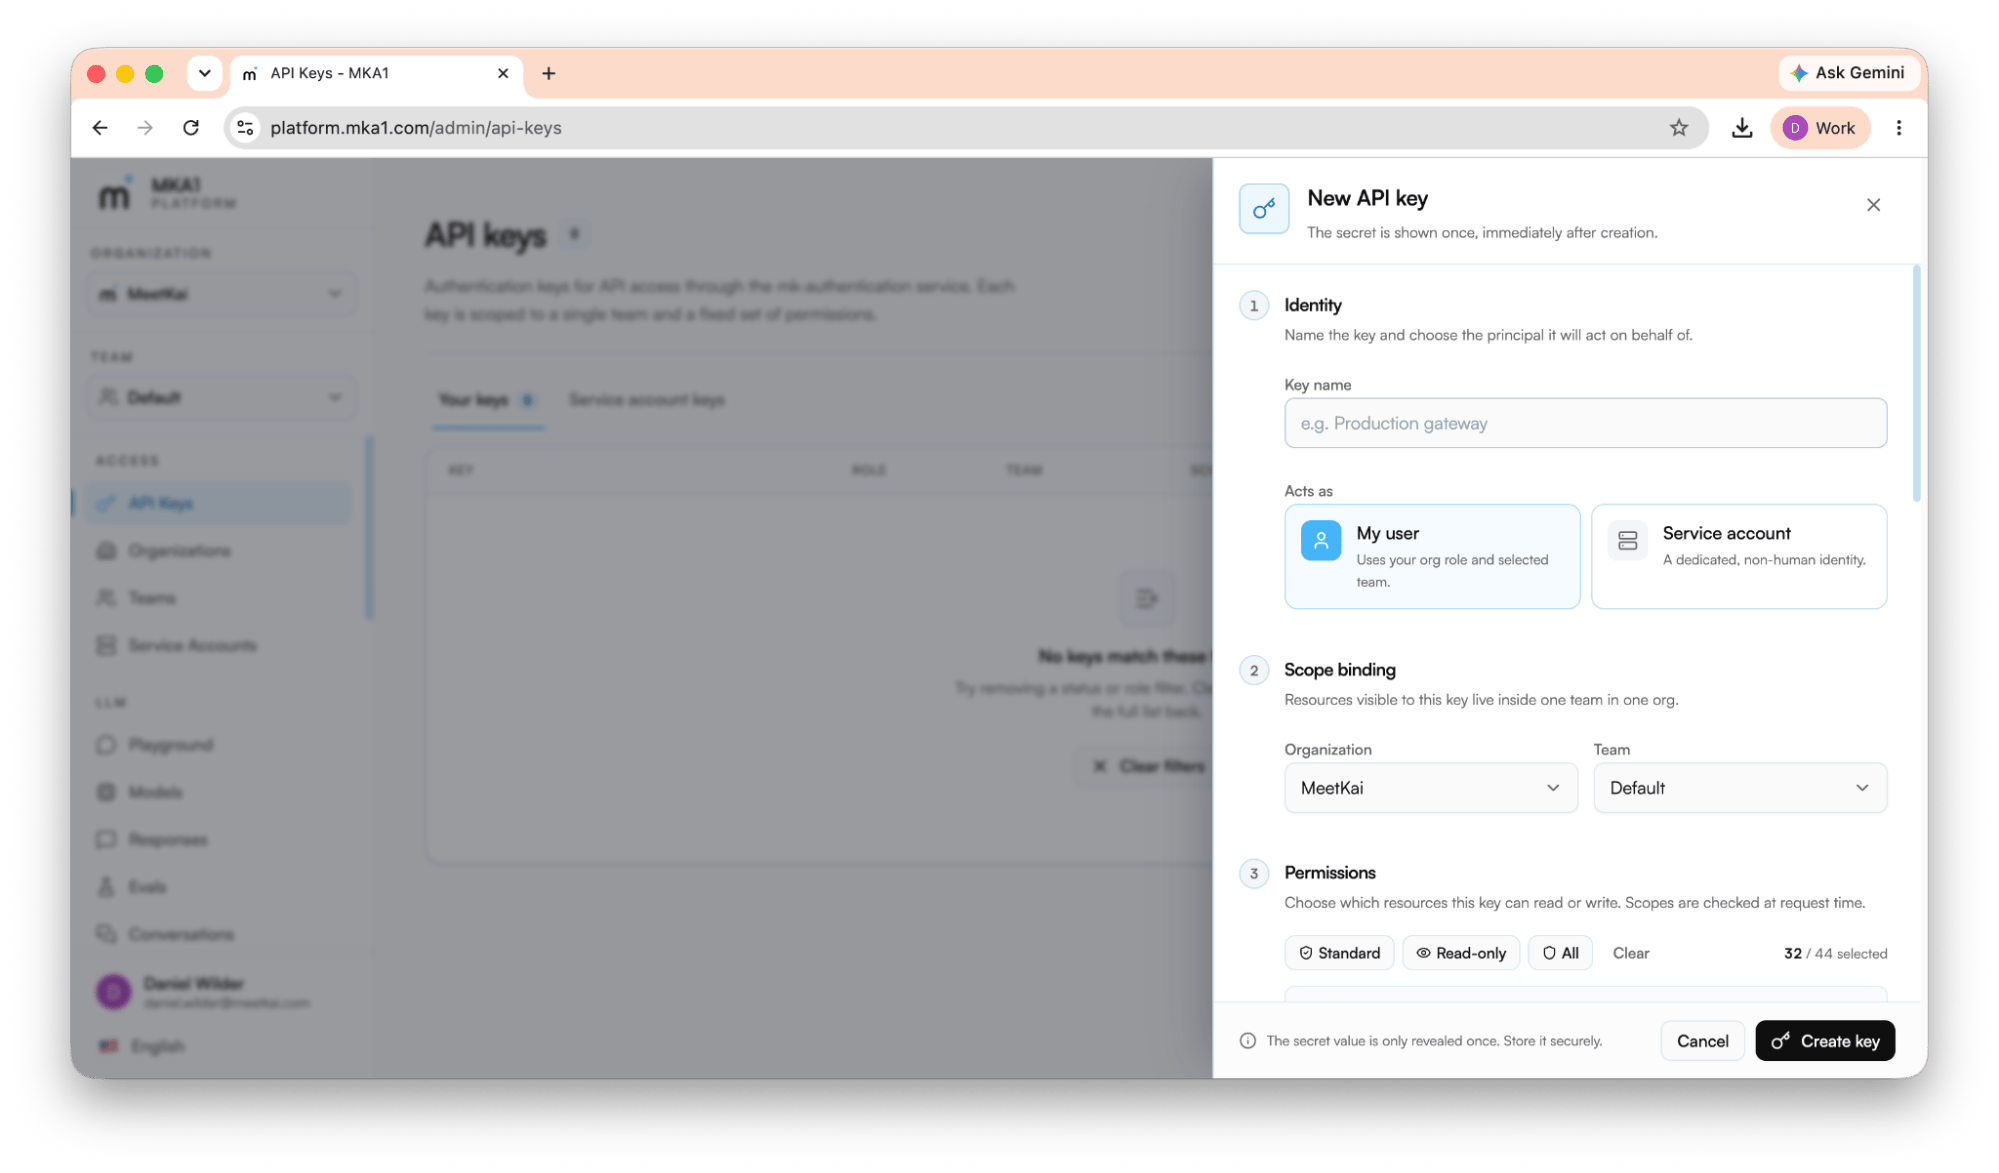 An API key is the credential your code sends on every request. In the console, open **Access → API Keys** and click **Create API key**. The form walks four steps.
### 1 · Identity
Name the key (e.g. Production gateway) and choose the principal it acts as: **My user** (uses your org role and selected team) or a **Service account** (a dedicated non-human identity. Service accounts are recommended for production use cases).
### 2 · Scope binding
Pick the **organization** and **team** the key belongs to. A key can only see resources inside that one team in that one org, so choose the team whose models, files, and agents this key should reach. Keys must be scoped to a team, and the **Default** team is already there. If you're a member who belongs to no team, ask an admin to add you to one before you create a key.
### 3 · Permissions (scopes)
Choose which resources the key can **read** and **write**. Scopes are checked on every request. Use a preset to move fast, then adjust:
* **Standard** - the everyday read/write scopes for building apps (responses, conversations, files, vector stores, prompts, agents, and more). For an admin, the preset also includes the repositories scopes.
* **Read-only** - every `read:` scope you're allowed to issue, and nothing else.
* **All** - every scope, including admin-only ones. Available only to org owners and admins.
Some scopes are **admin-only**: compute, repositories, budgets, batches, and fine-grained authorization (read and write), plus write access to the model registry and guardrails. These rows appear only if you're an owner or admin. Grant the narrowest set the key actually needs.
### 4 · Rate limiting (optional)
Optionally cap the key to a maximum number of requests per minute, hour, or day. The gateway enforces it and returns `429 Too Many Requests` before the request reaches a model, so over-limit calls cost nothing.
**Copy the secret now — it's shown only once**
When you click **Create key**, the full secret is revealed a **single time**. Copy it immediately and store it somewhere safe (a secrets manager or your .env). If you lose it, you can't view it again. Regenerate the key to get a new secret. Treat it like a password: never commit it to source control or expose it in browser code. Deleting a key immediately cuts off every application that uses it.
## Choose an identity
Use a [service account](/docs/service-accounts) for production applications. See [End-user identity](/docs/end-user-identity) when your server acts for application users, or [Short-lived tokens](/docs/short-lived-tokens) when a downstream client needs temporary access.
## Send your API key
Pass your API key as a bearer token.
```http theme={null}
Authorization: Bearer
```
Use `https://apigw.mka1.com` as the base URL.
```ts TypeScript SDK theme={null}
import { SDK } from '@meetkai/mka1';
const sdk = new SDK({ bearerAuth: 'Bearer ' });
const response = await sdk.llm.responses.create({
responsesCreateRequest: {
model: 'auto',
input: 'Write a short welcome message.',
},
})
```
```ts OpenAI SDK theme={null}
import OpenAI from 'openai';
const openai = new OpenAI({
apiKey: '',
baseURL: 'https://apigw.mka1.com/api/v1/llm/',
});
const response = await openai.responses.create({
model: 'auto',
input: 'Write a short welcome message.',
})
```
```python Python SDK theme={null}
from meetkai_mka1 import SDK
sdk = SDK(bearer_auth="Bearer ")
res = sdk.llm.responses.create(
model="auto",
input="Write a short welcome message.",
)
```
```csharp C# SDK theme={null}
using MeetKai.MKA1;
using MeetKai.MKA1.Types.Components;
using MeetKai.MKA1.Types.Requests;
var sdk = new SDK(bearerAuth: "Bearer ");
var res = await sdk.Llm.Responses.CreateAsync(new ResponsesCreateRequest()
{
Model = "auto",
Input = ResponsesCreateRequestInput.CreateStr("Write a short welcome message."),
});
```
```bash CLI theme={null}
export MKA1_BEARER_AUTH='Bearer '
mka1 llm responses create --model auto --input '"Write a short welcome message."'
```
```bash Bash theme={null}
curl https://apigw.mka1.com/api/v1/llm/responses \
--request POST \
--header 'Content-Type: application/json' \
--header 'Authorization: Bearer ' \
--data '{
"model": "auto",
"input": "Write a short welcome message."
}'
```
If your API key is missing, invalid, or does not have access to the requested resource, the MKA1 API returns an authentication or authorization error.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.